


Software Supply Chains
Software supply chains are the invisible production lines that turn source code and dependencies into the software artifacts users actually run, along with all the people, tools, and processes that shape them along the way.
[32x20v]
[x1b66l]
[p9rvuo]
A software supply chain is commonly defined as the set of components, libraries, tools, infrastructure, people, and processes used to develop, build, deliver, and maintain software.
[32x20v]
[x1b66l]
[p9rvuo]
[s28v12]
[saw93h]
Much like a physical supply chain moves raw materials into finished goods, a software supply chain “moves source code and dependencies from conception to deployment” and through ongoing maintenance.
[32x20v]
[b7fch9]
[saw93h]
It matters because any weakness or compromise in this chain—source code, open‑source dependencies, CI/CD pipelines, Build Systems, package registries, or distribution channels—can be exploited to reach potentially thousands of downstream users in a single event.
[9o37p1]
[p9rvuo]
[b7fch9]
[2k78e4]
[0n08hr]
[d4m6w9]
In practice, the term is central to modern discussions of software security, resilience, and governance, especially in ecosystems heavily dependent on open source and cloud‑native tooling.
[9o37p1]
[x1b66l]
[p9rvuo]
[s28v12]
[saw93h]
[0n08hr]
[1w61b4]
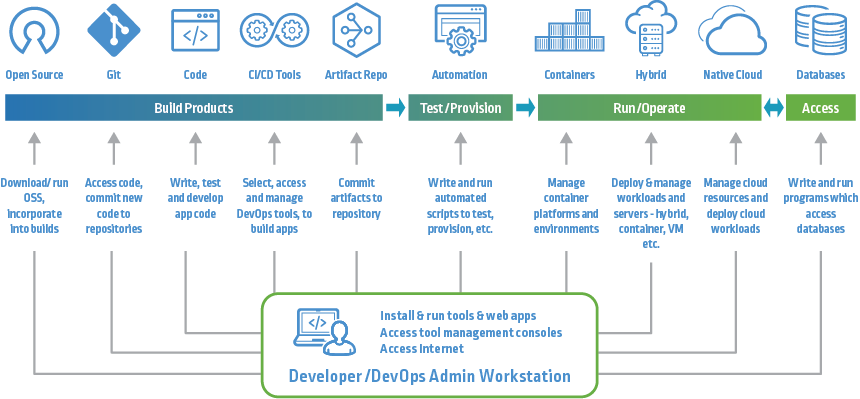
flowchart LR
A["Source code and version control"] --> B["Open source and third party dependencies"]
B --> C["Build tools and CI|CD pipelines"]
C --> D["Artifact repositories and package registries"]
D --> E["Deployment platforms and runtime environments"]
E --> F["End users and downstream systems"]
Defining and Describing Software Supply Chains
A widely cited description holds that a software supply chain is “the components, libraries, tools, and processes used to develop, build, and publish a software artifact.”
[x1b66l]
Other practitioners broaden this to “the entire set of processes, tools, components, people, and systems involved in developing, building, delivering, and maintaining software.”
[32x20v]
[p9rvuo]
[s28v12]
[saw93h]
In this view, a software supply chain encompasses not just code but the entire lifecycle of a piece of software, from ideation through development, testing, deployment, and ongoing maintenance.
[32x20v]
[p9rvuo]
[saw93h]
Authors frequently stress the analogy to manufacturing: just as physical supply chains move raw materials through factories and distribution networks, “a software supply chain moves code and digital artifacts — source, dependencies, build tools, and deployment pipelines.”
[b7fch9]
The “assets” in this chain include proprietary code, open‑source libraries, configurations, binaries, containers, build scripts, and infrastructure definitions, along with the systems that manipulate them.
[9o37p1]
[p9rvuo]
[b7fch9]
[saw93h]
[1w61b4]
Many security and engineering guides insist that the software supply chain also includes the human and organizational elements: “the entire ecosystem of people, processes, tools, code, and infrastructure that come together to produce and deliver software.”
[s28v12]
This broader framing highlights that governance practices, access controls, and organizational culture are part of the supply chain surface, not merely add‑ons.
[p9rvuo]
[s28v12]
[0n08hr]
[1w61b4]
Some practitioners define software supply chains operationally by the stages of import, build, distribute, and consume.
[saw93h]
In this flow, organizations import third‑party tools and libraries, build artifacts in CI/CD systems, distribute those artifacts internally or to customers, and then consume or run them in development, test, and production environments.
[saw93h]
Each stage introduces distinct dependencies and potential attack or failure points.
[9o37p1]
[p9rvuo]
[2k78e4]
[5vbuef]
[0n08hr]
[1w61b4]
At a conceptual level, many commentators emphasize that “at its core, the software supply chain is about trust: trusting every component and tool that participates in creating and delivering software to end users.”
[32x20v]
[p9rvuo]
[s28v12]
[le8mtu]
[2k78e4]
[0n08hr]
This places software supply chains squarely at the intersection of software engineering, open‑source ecosystems, and security, especially in contexts where transitive dependencies and automated build pipelines can propagate a single upstream compromise to large populations of downstream systems.
[9o37p1]
[p9rvuo]
[b7fch9]
[2k78e4]
[gomi3t]
[0n08hr]
[d4m6w9]
[1w61b4]
Uses in Context
- Security practitioners use the term to describe the full attack surface of modern development, noting that “the modern software supply chain spans source code, open‑source dependencies, CI/CD pipelines, build systems, cloud infrastructure, and third‑party services.” [9o37p1] [x1b66l] [p9rvuo] [s28v12] [2k78e4] [0n08hr] [1w61b4]
- Security writing often frames software supply chain security as “the practice of protecting the processes, tools, and artifacts used to build, package, distribute, and run software,” tying together build, artifact, and runtime controls to ensure authenticity, integrity, and traceability. [le8mtu] [5vbuef] [saw93h] [0n08hr] [1w61b4]
- Discussions of supply chain attacks use the term to distinguish indirect compromise, explaining that “software supply chain attacks compromise the build, distribution, or update mechanisms of software rather than attacking end targets directly” and “compromise a dependency, tool, build system, or distribution channel that the target trusts.” [2k78e4] [0n08hr] [d4m6w9] [1w61b4]
- Policy and compliance materials use “software supply chain” to frame obligations like producing a Software Bill of Materials (SBOM)—defined as “a machine-readable inventory of every component, library, and dependency inside a software application”—as a way to provide transparency into the chain. [gomi3t] [0n08hr]
- Application security guides invoke the term to explain the breadth of components involved in modern applications, noting that developers “put apps and websites together using various interdependent components and processes, which together we call the software supply chain.” [1w61b4]
History of Use
Origins
The phrase “software supply chain” appears in technical and security discourse by analogy to traditional supply chains, but early uses were often descriptive rather than formalized in a single foundational paper.
[x1b66l]
[b7fch9]
[saw93h]
The concept gained specific security relevance as practitioners noticed that compromises in upstream libraries and build systems could propagate malicious code to many downstream users, leading to early discussions of software supply chain attacks and defenses in community blogs, conference talks, and security advisories rather than primarily in big‑vendor marketing materials.
[b7fch9]
[2k78e4]
[saw93h]
[0n08hr]
[d4m6w9]
[1w61b4]
Wikipedia’s contemporary definition—“the components, libraries, tools, and processes used to develop, build, and publish a software artifact”—captures the consensus that emerged from these practitioner and open‑source discussions.
[x1b66l]
Evolution
- Pre‑2010s: early dependency and build-chain concerns. As software projects increasingly reused third‑party libraries and automated build tools, early open‑source and academic communities began highlighting risks associated with trusted dependencies and build environments, laying the groundwork for the idea that software has a “supply chain” analogous to physical manufacturing. [b7fch9] [gomi3t] [saw93h] [0n08hr]
- 2010s: formalization in security discourse and tooling. During the 2010s, the term “software supply chain” became more widely used in security and DevOps communities to describe the end‑to‑end pipeline from code to deployment, emphasizing that a “single upstream compromise can spread to thousands of downstream users almost instantly” and prompting early best‑practice guides and tooling around dependency management and build integrity. [b7fch9] [2k78e4] [gomi3t] [saw93h] [0n08hr] [1w61b4]
- Late 2010s–early 2020s: high‑profile attacks drive mainstream adoption. High‑impact incidents such as supply chain compromises at software vendors and open‑source ecosystems (including attacks that leveraged trusted update mechanisms and dependencies) demonstrated how “software supply chain attacks infiltrate software vendor systems to deliver compromised software to thousands of customers,” catapulting the term into mainstream security discourse and policy discussions. [2k78e4] [gomi3t] [0n08hr] [d4m6w9] [1w61b4] This period also saw the popularization of SBOMs and comprehensive “software supply chain security” frameworks as responses. [gomi3t] [saw93h] [0n08hr]
- Mid‑2020s: broadened ecosystem and standards focus. Recent materials frame software supply chain security as an “end‑to‑end discipline, not a single tool,” covering everything from import of open‑source packages to CI/CD automation, runtime environments, and incident response. [saw93h] [0n08hr] [1w61b4] Organizations have adopted defense‑in‑depth approaches, standardizing pipeline templates, automated scanning, and SBOM generation to strengthen their software supply chains, while community projects and startups provide specialized tools for monitoring dependencies, scanning artifacts, and modeling supply chain risk. [9o37p1] [p9rvuo] [s28v12] [le8mtu] [gomi3t] [5vbuef] [5ka1b6] [saw93h] [0n08hr] [1w61b4]
Best Real-World Examples
- Cycode provides a platform explicitly focused on securing the modern software supply chain, describing it as spanning “source code, open-source dependencies, CI/CD pipelines, build systems, cloud infrastructure, and third-party services” and offering tools to identify and remediate risks across this continuum. [9o37p1]
- ActiveState Platform exemplifies a managed approach to software supply chains by curating open‑source languages and dependencies, controlling builds, and providing guidance on “supply chain best practices” to reduce the risk that a single upstream compromise will propagate to downstream users. [b7fch9] [saw93h]
- PuppyGraph illustrates how smaller vendors articulate holistic software supply chains, defining them as “the entire set of processes, tools, components, people, and systems” in software development, and positioning graph‑based analysis as a way to understand complex dependency relationships and trust flows. [32x20v]
- DevSecOpsNow offers practitioner‑oriented guidance on “software supply chain security,” framing it as a systemic discipline that protects “the processes, tools, and artifacts used to build, package, distribute, and run software,” and providing examples of attacks and controls across build, artifact, and runtime stages. [le8mtu] [5vbuef]
- CHS Software Supply Chain Security Guide presents a stage‑based view of software supply chains, mapping stages, assets, representative threats, and primary controls, and defining software supply chain attacks as compromising dependencies, tools, build systems, or distribution channels that targets trust. [2k78e4]
- Reflectiz demonstrates how application security vendors conceptualize web and SaaS software supply chains, highlighting how developers “put apps and websites together using various interdependent components and processes, which together we call the software supply chain,” and categorizing supply chain attacks across source code, dependencies, build pipelines, and runtime environments. [1w61b4]
- Wiz Academy provides educational material on supply chain attacks, including software-focused examples such as Kaseya and Codecov, illustrating how threat actors compromise trusted third‑party components and workflows to infiltrate downstream systems in cloud and SaaS contexts. [d4m6w9]
Case Studies
Open-source dependency compromise and downstream impact
In one widely discussed pattern of software supply chain compromise, attackers target upstream open‑source dependencies rather than individual end organizations, knowing that “a single upstream compromise can spread to thousands of downstream users almost instantly.”
[b7fch9]
[2k78e4]
[gomi3t]
[0n08hr]
Practitioner guides explain that a software supply chain attack “compromises a dependency, tool, build system, or distribution channel that the target trusts, rather than attacking the target directly,” allowing malicious payloads to “ride in on a routine” update or dependency resolution.
[2k78e4]
[0n08hr]
[d4m6w9]
In these scenarios, an attacker might upload a malicious package that mimics a popular library (typosquatting) or gain access to a maintainer account and inject malicious code into a legitimate package.
[2k78e4]
[gomi3t]
[5vbuef]
[0n08hr]
[1w61b4]
When downstream organizations import or update the affected dependency as part of their normal build process, the malicious code becomes integrated into their software artifacts, potentially exfiltrating secrets, opening backdoors, or otherwise compromising systems at scale.
[2k78e4]
[gomi3t]
[0n08hr]
[d4m6w9]
[1w61b4]
This case pattern illustrates how the software supply chain—particularly public package registries and transitive dependencies—constitutes an attack surface, and why SBOMs, behavioral scanning, and new‑publisher heuristics are recommended controls.
[2k78e4]
[gomi3t]
[0n08hr]
CI/CD pipeline compromise in a modern DevOps environment
Another key case pattern centers on attacks against CI/CD Pipelines and build infrastructure, which supply chain security guides classify as “build and pipeline attacks” that “compromise CI/CD systems or build plugins to inject malicious artifacts.”
[9o37p1]
[p9rvuo]
[le8mtu]
[5vbuef]
[0n08hr]
[1w61b4]
In such incidents, attackers obtain access to build servers or pipeline configurations, modifying scripts or inserting malicious steps so that every build produced by the pipeline includes attacker‑controlled code, even when the source repositories themselves appear clean.
[9o37p1]
[p9rvuo]
[le8mtu]
[5vbuef]
[0n08hr]
[1w61b4]
Security best‑practice documents describe this as part of the broader software supply chain because the pipeline, build tools, artifact repositories, and release automation collectively constitute the mechanisms by which source code becomes deployed software.
[9o37p1]
[p9rvuo]
[s28v12]
[le8mtu]
[5vbuef]
[5ka1b6]
[saw93h]
[0n08hr]
[1w61b4]
A compromised pipeline can therefore impact many services and customers simultaneously, especially in organizations with centralized CI/CD infrastructure. Recommended responses include standardizing “governed pipeline templates,” enforcing secure compute environments, automatically injecting static analysis and SBOM generation, and applying compliance gates such as two‑person pull‑request sign‑offs and code signing to the software supply chain.
[5ka1b6]
[saw93h]
[0n08hr]
[1w61b4]
This case pattern illustrates how securing software supply chains requires not only dependency hygiene but also robust controls over automation and infrastructure.
Web application and third-party script ecosystem risks
Web application security research has also adopted the software supply chain lens to describe how modern websites rely on extensive networks of third‑party scripts, SDKs, and services.
[1w61b4]
Reflectiz, for example, notes that developers assemble apps and websites from “various interdependent components and processes, which together we call the software supply chain,” including source code, version control systems, open‑source and third‑party dependencies, CI/CD pipelines, artifact repositories, and runtime environments such as browsers and content delivery networks.
[1w61b4]
In this context, a compromise of a third‑party script, tag manager, or SaaS integration can propagate malicious behavior across many customer sites that include the affected component.
[d4m6w9]
[1w61b4]
Supply chain attacks here may resemble dependency attacks (e.g., a compromised npm package used in front‑end builds) or runtime environment attacks, which target the deployment platforms and containers (including browsers executing scripts) after code is built and deployed.
[d4m6w9]
[1w61b4]
This case pattern underscores that software supply chains extend beyond server-side code into client-side ecosystems and managed services, and that software supply chain security must address third‑party governance and runtime monitoring as much as build-time controls.
[2k78e4]
[0n08hr]
[d4m6w9]
[1w61b4]